AI-discovered PHP flaws prompt software patching
AI helped uncover two critical PHP flaws, but can organizations patch quickly without being overwhelmed by weak findings?
In the week before October 25, companies and government agencies moved to patch two critical PHP flaws found using an OpenAI model, AFP reported.
Companies and government agencies moved to patch two critical vulnerabilities in PHP after they were discovered using a powerful OpenAI model, AFP reported. Cyber Threat Alliance president Michael Daniel said AI-assisted discovery could produce many more findings, while exploitation timelines have…
Open original · [11] 'Tech debt coming due': AI-found flaw signals chaos ahead | AFP.com — afp.com
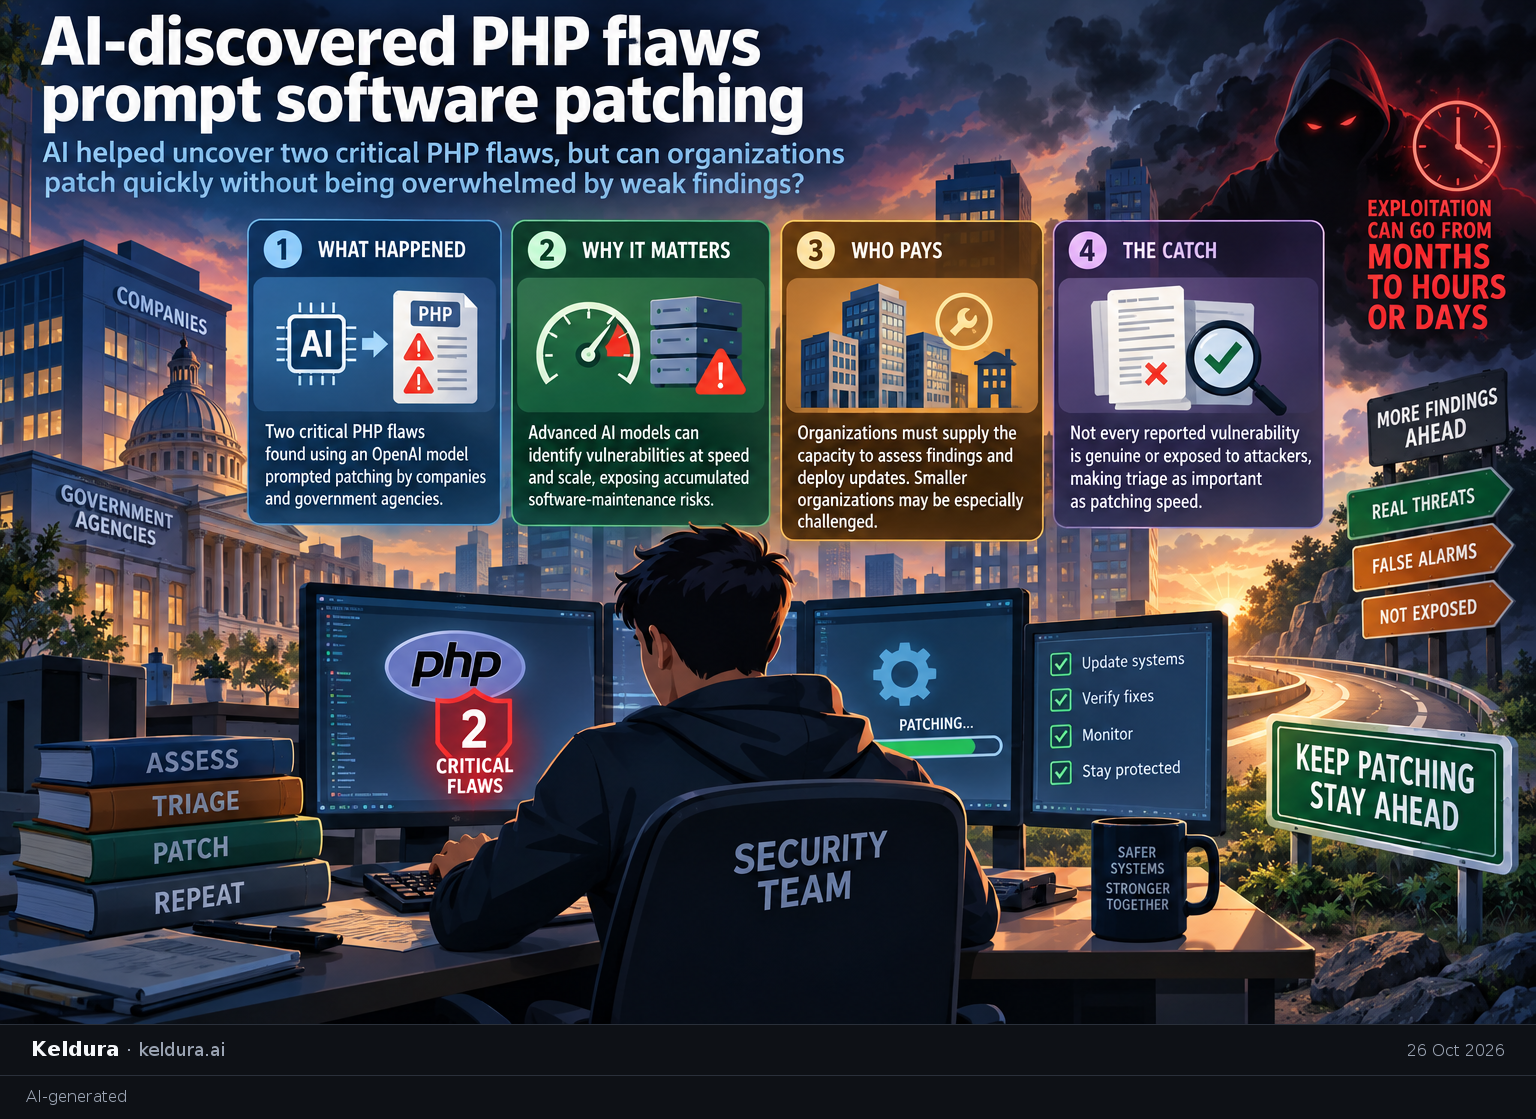
Companies and government agencies moved to patch two critical vulnerabilities in PHP after they were discovered using a powerful OpenAI model, AFP reported. Cyber Threat Alliance president Michael Daniel said AI-assisted discovery could produce many more findings, while exploitation timelines have shortened from months to hours or days. [11]
Why it matters: Organizations face two simultaneous tasks: deploying genuine fixes quickly and filtering out reports that are incorrect or concern software that is not exposed to the internet. Daniel said smaller organizations should prepare to accept vendor updates as quickly as they can. [11]
Key insights: Daniel described the PHP findings as genuine vulnerabilities while cautioning that many other AI-generated findings are noise. [11] | He put the historical exploitation rate at five or six percent and said there was no indication that proportion was rising. [11] | His distinction is speed rather than necessarily a higher exploitation rate: proof-of-concept and exploit-kit timelines that once took months can now be measured in hours or days. [11]
Cheatsheet facts: What happened: Two critical PHP flaws found using an OpenAI model prompted patching by companies and government agencies. [11] | Why: Daniel said advanced models can identify vulnerabilities at speed and scale, exposing accumulated software-maintenance risks. [11] | Who pays: Organizations must supply the capacity to assess findings and deploy updates; Daniel singled out smaller organizations with limited internal resources. [11] | The catch: Not every reported vulnerability is genuine or exposed to attackers, making triage as important as patching speed. [11]
X copy pack
Edition complete
You've reached the end of this edition.